Deployment
Cloud, on-premise or hybrid — air-gap capable where SaaS is ruled out.
Access Management, Identity Governance and Privileged Access — eighteen capabilities sharing one identity fabric, one policy engine and one audit trail, instead of three disconnected products.
Single sign-on, risk-based authentication and a personalised launchpad — so users get in fast, and only ever the way policy allows.
One sign-in across every application, via SAML 2.0 and OIDC.
Risk-based multi-factor with configurable factors, policies and network zones.
WebAuthn passkeys and two-factor sign-in, with self-service password reset.
A personalised portal listing every application a user is entitled to.
Go beyond passwords & OTPs with identity-bound security.
Zetect’s biometric MFA requires a fingerprint or facial scan to verify the user’s identity in real time. This ensures that even if a device or password is compromised, attackers cannot gain access without the unique biological traits of the authorized individual.
From the moment an identity is created to the moment it leaves, access is requested, reviewed, and retired automatically — with the evidence produced as a by-product.
Aggregate and correlate users, groups and attributes from every connected source.
Automated joiner, mover and leaver provisioning across every connected application.
Self-service catalog with configurable approval policies and an approval queue.
Scheduled review campaigns, including orphan-account and full-identity reviews.
Toxic-combination rules evaluated before access is granted, not after.
Access granted and revoked automatically as attributes and group membership change.
Credentials vaulted, privilege granted just-in-time, and every session brokered and recorded — without installing anything on the target itself.
Privileged credentials vaulted and rotated automatically — no shared admin passwords.
Privilege granted against an asset for the moment it is needed, then revoked.
Agentless RDP and SSH, brokered without installing anything on the target.
Full recording, live monitoring and one-click termination of any privileged session.
The connective tissue underneath every module above — one audit trail, one mapping engine, and agentless connectivity to everything you already run.
Authentication, entitlement and privileged events correlated on one timeline.
A declarative engine for lookups, decisions and pipelines — no connector code.
Agentless connectivity to apps and assets, with a connector build toolkit.
Operational and compliance reporting drawn from the same single data model.
Point tools leave seams, and attackers live in the seams between login, entitlement and privilege. Because all three disciplines run on one identity fabric, every authentication, access grant and keystroke lands on a single correlated timeline.
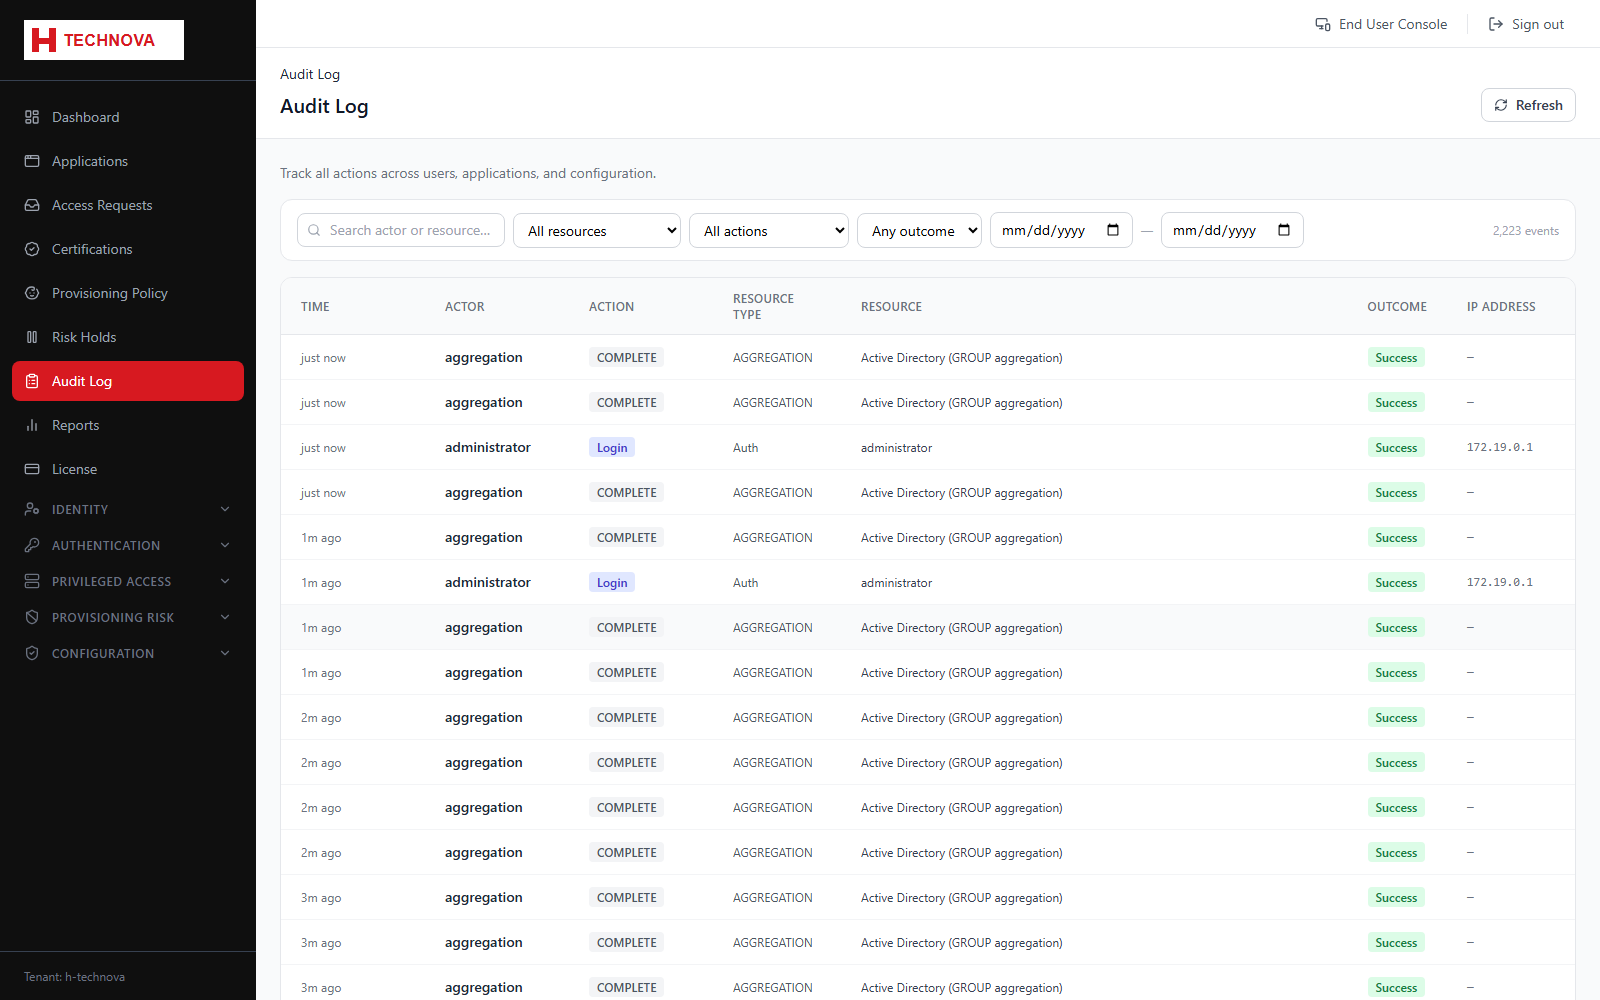
Cloud, on-premise or hybrid — air-gap capable where SaaS is ruled out.
SAML 2.0, OIDC, SCIM and REST APIs into the systems you already run.
Agentless throughout, including brokered RDP and SSH — no target footprint.
Evidence that maps to ISO 27001, SOC 2, PCI-DSS, HIPAA, SOX, GDPR and NIST 800-53.
Start with one module and add the others later — no migration project in between.
See how Zetect can be tailored to your environment